Accounts are isolated from one another
Each organization's data is tied to its own account. The system does not allow a user of one organization to access another organization's leads, messages, or files.
Security and data
In health tourism, you work with sensitive information such as patient photos, phone numbers, and conversation history. Here, we describe without exaggeration which measures are actually implemented in Websens CRM.
Measures in place
Each organization's data is tied to its own account. The system does not allow a user of one organization to access another organization's leads, messages, or files.
Users other than administrators are granted only defined permissions: each action—such as viewing leads, replying to messages, exporting, or deleting—is a separate permission. A user can be restricted to see only the leads and channels assigned to them.
Each user can add two-step verification to their own account. An administrator can make it mandatory for all users in the organization.
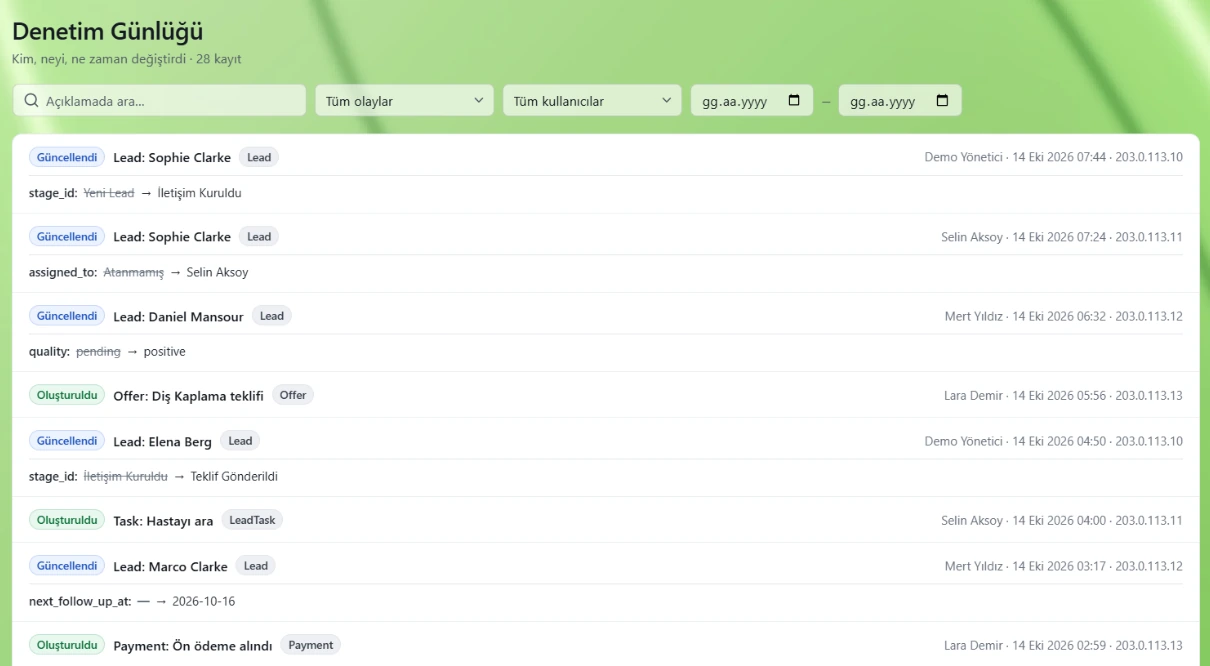
Create, update, and delete operations performed in the panel are logged with who performed them and when. Administrators view the log from the panel.
We store Meta and TikTok connection tokens and your own AI key encrypted in the system. Passwords are kept in an irreversible form (hashed).
Uploaded photos and documents are not kept at a public address; they are served only to logged-in and authorized users, after verification.
Events coming from Meta and TikTok go through signature verification; requests with invalid signatures are not processed. Rate limiting is applied to public endpoints.
A daily backup of the database is taken and recent backups are retained. Backups and system health are regularly audited.
You can export leads as Excel/CSV and download your account data. When you request it, your account is permanently deleted with all its data.
Transparency
We do not yet have an independent security certification such as ISO 27001 or SOC 2, and we do not act as if we do. Instead, we clearly state the controls we implement, the infrastructure providers we use, and who is responsible for the data.
FAQ
Websens CRM runs in Hostinger's European data centers. The full list of our providers and the data transferred to each are set out in the Privacy Policy.
For the data of your patient candidates, you, the organization, are the data controller; Websens acts as the data processor only on your instructions and to provide the service. Details are in the Privacy Policy.
Yes. When the AI chatbot is enabled, the relevant chat text is sent to the AI provider to generate a response. If you never enable the feature, no data goes to the AI provider. If you wish, you can use your own provider key. You must inform your patients about this.
No. Payment is completed on PayTR’s own secure page; card information never enters the Websens system.
We do not currently. That is why, instead of making claims, we clearly document each of the controls above. For your security questions or assessment forms, you can email info@websens.co.
14 days free, no credit card required. See permissions, the audit log, and two-step verification in your own account.
Last updated: